NAverstali 152
Our own product: it finds small-business sites that break Russia's personal data law and walks the client from first call to the fix.
- Year
- 2026
- What we did
- Design and code
- What was needed
Studios need clients with a clear problem. A site at risk of a fine is exactly that, but finding them by hand is slow, and explaining it to an owner without evidence goes nowhere.
- What we did
A Node.js monolith with a queue in PostgreSQL: collection, checks, the LLM policy pass and the weekly re-check all run as background jobs. Each studio only sees its own clients. The model runs on our own server, so no data leaves it.
- More detail
Since 2025 the fines under Russia's personal data law have grown many times over, and most small-business sites don't even have a privacy policy. We built a tool that finds them.
It collects sites by region from OpenStreetMap, checks the home page for 9 technical signs (HTTPS, a policy, consent on forms, a cookie notice, Google Analytics, foreign forms and trackers) and reads the policy text with a language model for 7 more. The result is a risk score from 0 to 10 with evidence: what was found and where.
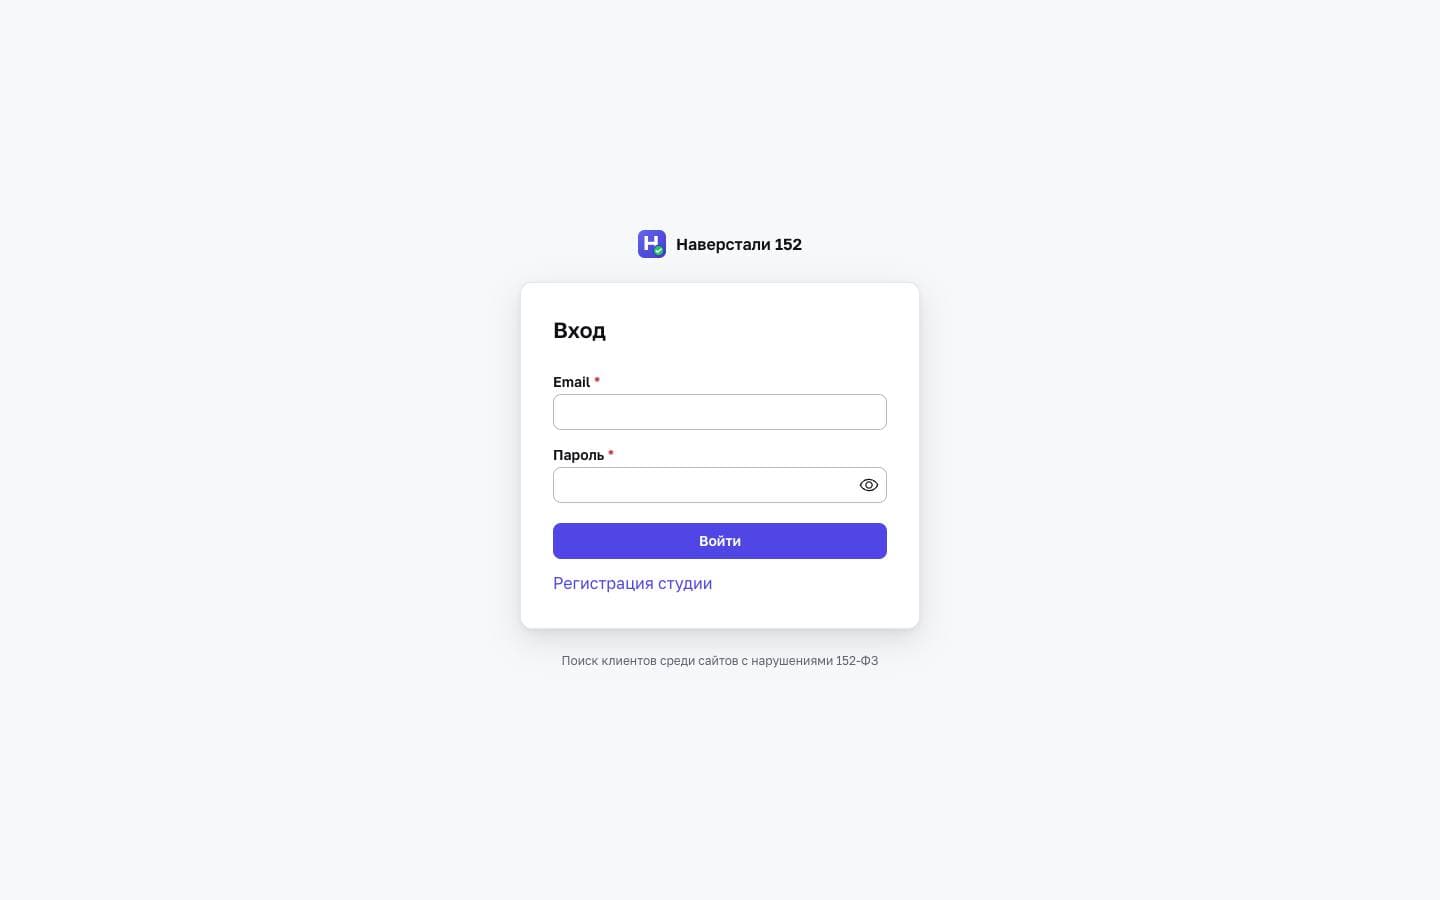
On top sits a small CRM: claim a client for your studio, log calls, export a PDF report with the studio's logo, re-check a week later and show what got fixed.
What it looks like
How it turned out
It runs in our own studio: a manager opens the table, picks a high-risk site and calls with a report in hand.
Built with
Node.jsTypeScriptFastifyPrismaPostgreSQLpg-bossReactMantineLLM
Got a similar job? Tell us
Write a few words about the project. We read it ourselves and reply with a rough price and when we can start.
Fill in the brief